
What is Authentication?
Updated: 3 days ago
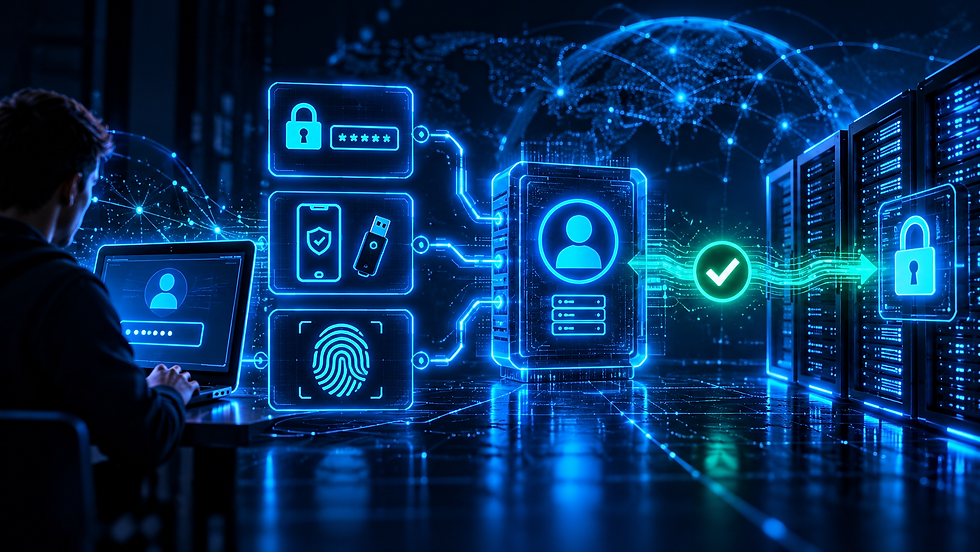
Authentication is the process of verifying a claimed identity before a system accepts that identity as authenticated. In everyday terms, it is how a website, app, computer or network checks that you can prove control of an authenticator associated with an account or device.
A password is one familiar authenticator, but authentication can also involve passkeys, security keys, one-time codes, cryptographic keys and biometric characteristics. Strong authentication is especially important because a username or account name identifies the identity being claimed, but does not by itself prove who is making the claim.

What is authentication in simple terms?
Authentication answers a practical question: can this person, device or service prove that it controls the authenticator expected for the identity it is claiming?
For example, entering an email address tells a service which account you want to use. Supplying the correct password, approving a passkey prompt or using a registered security key provides evidence that the service can verify. If the check succeeds, the service can establish an authenticated session.
Authentication is therefore closely connected with encryption, but they are not the same thing. Encryption protects information from unauthorised reading or alteration in particular contexts. Authentication is about verifying an identity claim or authenticator.
How does authentication work?
Claim an identity: the user, device or service indicates which identity it wants to use.
Present authentication evidence: an authenticator such as a password, passkey, security key or other credential is used.
Verify the evidence: the system checks whether the presented evidence satisfies its authentication requirements.
Establish the authenticated state: if verification succeeds, the system can create a session or issue credentials representing the authenticated identity.
Apply access policy: separate authorisation rules determine what that authenticated identity is permitted to do.
The exact process varies considerably between systems. A local computer login, online banking session, WiFi network, VPN and machine-to-machine API can all authenticate identities in different ways.
What are authentication factors?
Authentication factors describe different categories of evidence. A common way to explain them is:
Something you know: for example, a password or PIN.
Something you have: for example, a phone, authenticator device, smart card or hardware security key.
Something you are: a biometric characteristic used by the authentication system, such as a fingerprint or face measurement.
Using two steps does not automatically mean two-factor authentication. If both steps rely on the same factor category, the process may be multi-step without being genuinely multi-factor.
What is multi-factor authentication (MFA)?
Multi-factor authentication requires authentication using more than one distinct factor. The purpose is to reduce reliance on a single authenticator. If an attacker learns a password, for example, they may still be unable to authenticate without the additional factor.
MFA can substantially improve account security, but not every MFA method offers the same resistance to phishing or account takeover. Recovery processes also matter because a weak recovery route can undermine a strong login process.
What is the difference between authentication and authorisation?
Authentication and authorisation are related but separate controls. Authentication verifies the identity claim. Authorisation decides what the authenticated identity is allowed to access or do.
This distinction is important in Zero Trust networking, where successful authentication does not mean unlimited trust. Access can still be restricted according to identity, device, resource, context and policy.
Passwords and authentication
Passwords remain widely used because they are simple to deploy, but they create familiar risks including reuse, weak choices, phishing and credential theft. Services can reduce those risks with controls such as MFA, secure password handling, rate limiting, monitoring and phishing-resistant authentication methods.
A secure connection also matters when authentication data travels across a network. TLS protects many internet connections, while HTTPS uses TLS to secure HTTP traffic between a client and web server.
What are passkeys?
Passkeys use public-key cryptography rather than requiring a shared password to be typed into the service. The private key remains under the user's control on an authenticator, while the service stores the corresponding public-key information needed for verification.
Because the cryptographic credential is associated with the legitimate service rather than something a user manually types into any convincing login page, properly implemented passkeys can provide strong resistance to conventional credential phishing.
What is device authentication?
Authentication is not limited to human users. Devices and services can authenticate to each other using certificates, cryptographic keys, tokens and other mechanisms. This is common in enterprise networks, APIs, cloud platforms and managed infrastructure.
A VPN may authenticate a user, a device or both before permitting a tunnel to be established. The precise method depends on the VPN technology and configuration.
Does authentication make an account completely secure?
No. Authentication is one part of security. An authenticated account can still be compromised through malware, stolen sessions, insecure recovery procedures, social engineering, excessive permissions or vulnerabilities elsewhere in the system.
Good security therefore combines authentication with appropriate authorisation, encrypted communications, monitoring, secure recovery, software updates and other controls.
Authentication and broadband networks
Authentication appears throughout modern broadband and home networking even when it is not obvious to the user. You may authenticate to a router administration interface, WiFi network, VPN service, ISP account, email service, cloud application or remote server.
Network controls such as a firewall can restrict traffic, but allowing a connection through a network boundary is not the same as authenticating the identity using the application or service.
How can authentication be made stronger?
Use multi-factor authentication for important accounts where available.
Prefer phishing-resistant authentication methods such as passkeys or hardware security keys where they are supported and appropriate.
Use unique passwords when passwords are required, ideally managed with a reputable password manager.
Protect account recovery routes and backup authentication methods.
Keep devices and authentication software updated.
Treat unexpected login prompts and approval requests as suspicious.
Limit repeated failed attempts and monitor unusual authentication activity where the system supports it.
Frequently asked questions about authentication
Is a username authentication?
Usually not by itself. A username or account identifier normally tells the system which identity is being claimed. Authentication requires evidence that verifies the claim.
Is a password the same as authentication?
No. A password is one type of authenticator or authentication secret. Authentication is the wider verification process.
Is two-step verification always MFA?
No. Two steps can use the same factor category. MFA requires more than one distinct authentication factor.
Is authentication the same as authorisation?
No. Authentication verifies an identity claim. Authorisation determines what the authenticated identity is permitted to access or do.
Does HTTPS authenticate the person using a website?
Not normally. HTTPS uses TLS to authenticate the server to the client in the usual web model and to protect the connection. A website uses its own login or authentication process to authenticate the user.
Technical references
NIST Digital Identity Guidelines provide detailed guidance on digital identity, authentication and authenticator assurance.
The W3C Web Authentication specification defines the WebAuthn API used for strong public-key credentials on the web.
To explore the related technical concepts used in this Authentication guide, visit our broadband terminology guide.
