
What is IDS (Intrusion Detection System)?
Updated: 3 days ago
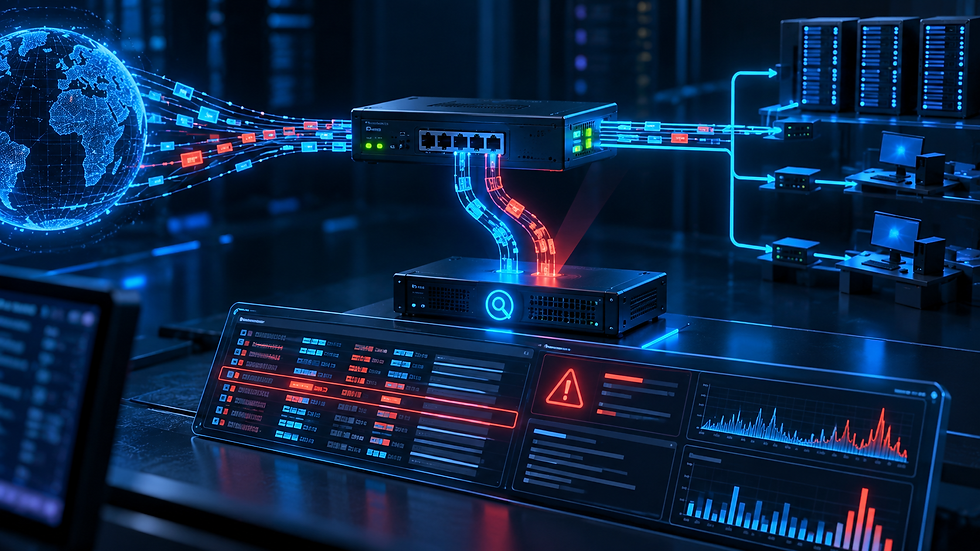
An IDS, or Intrusion Detection System, is a security system that monitors network traffic or activity on a computer and analyses it for signs of suspicious or potentially malicious behaviour. When it detects activity that matches its detection logic, it records the event and can raise an alert so somebody or another security system can investigate.
The most important distinction is that detection is not the same as prevention. A traditional IDS is primarily an observer. It can identify and report suspicious activity, but it does not automatically mean the traffic was blocked. An Intrusion Prevention System, or IPS, adds the ability to attempt to stop matching activity, commonly by operating inline with the traffic.

How does an Intrusion Detection System work?
An IDS collects information from a point where it can observe useful activity. A network IDS may receive a copy of network traffic from a switch mirror port, network tap or virtual networking layer. A host IDS runs on or monitors an individual system and can examine events such as logins, processes, file changes and other host activity.
The IDS then analyses what it sees using one or more detection methods. If an event or traffic pattern meets the conditions for an alert, the system records information about it and generates an alert for investigation. NIST describes intrusion detection as monitoring events in a computer system or network and analysing them for signs of possible incidents.
Observe: collect network traffic, host events, logs or other relevant telemetry.
Analyse: compare the observed activity with rules, known indicators, behavioural baselines or other detection logic.
Detect: identify activity that meets the configured conditions for suspicion.
Record: preserve useful event information so the activity can be investigated.
Alert: notify an administrator, security platform or monitoring workflow.
What is the difference between NIDS and HIDS?
The two terms describe where the intrusion detection visibility comes from. Neither is automatically better. They see different parts of an incident and can complement each other.
NIDS, Network Intrusion Detection System: monitors network traffic for particular network segments or devices. NIST describes NIDS as performing packet sniffing and network traffic analysis to identify suspicious activity and record relevant information.
HIDS, Host Intrusion Detection System: monitors an individual computer, server or endpoint. It can observe events that may never be visible in network packets, including local processes, authentication events and file changes.
Hybrid monitoring: organisations can combine network and host telemetry so an incident can be examined from more than one viewpoint.
How does an IDS detect suspicious activity?
Detection systems do not all use the same method. A practical IDS may combine several techniques, and the quality of its results depends on the rules, models, context, traffic visibility and tuning available to it.
Signature-based detection
Signature-based detection looks for known patterns associated with particular threats or behaviours. A network rule might inspect protocol fields, connection characteristics or visible payload content. This can be precise for known activity, but a signature cannot detect something it has not been written or generalised to recognise.
Anomaly-based detection
Anomaly-based detection looks for activity that differs from an expected baseline or behavioural model. It can help surface unusual activity that has no exact known signature, but unusual does not automatically mean malicious. Poor baselines can create noise.
Stateful protocol analysis
Some systems understand how particular protocols are expected to behave and can flag activity that violates those expectations. This is more context-aware than simply matching isolated bytes, but it requires accurate protocol handling and enough processing capacity.
IDS vs IPS: what is the difference?
An IDS is designed to detect and alert. An IPS includes intrusion detection capabilities and can also attempt to stop detected activity. NIST defines an IDPS as software that monitors events for possible incidents and can attempt to stop them.
IDS: normally observes traffic or host activity and generates alerts.
IPS: normally sits in a position where it can take action on traffic, such as dropping or rejecting matching packets.
Firewall: enforces traffic policy. Some modern firewalls also contain IDS or IPS capabilities, but firewalling and intrusion detection are not interchangeable concepts.
SIEM: collects and correlates security information from multiple sources. An IDS can feed alerts into a SIEM, but a SIEM is not simply another name for an IDS.
Suricata provides a useful real-world example of the distinction. Its documentation describes passive IDS mode separately from IPS mode, where it can operate inline and use drop or reject rules against unwanted traffic.
Where does packet inspection fit into IDS?
A network IDS needs visibility into network traffic, so packet inspection is central to many NIDS deployments. The system may inspect packet headers, connection state, protocols and, where visible, application data. This overlaps with the broader concept of packet inspection, but packet inspection itself is not automatically intrusion detection.
Encryption changes what a network IDS can see. With properly encrypted application traffic, an intermediary sensor generally cannot simply read the protected application payload. It may still see metadata and unencrypted protocol information, and some managed environments deliberately terminate or decrypt traffic at controlled inspection points. The visibility available depends on the protocol, architecture and where the sensor is placed.
Where should a network IDS be placed?
Placement determines what a NIDS can observe. A sensor positioned at the broadband edge sees different traffic from one monitoring a server VLAN, data-centre segment or internal east-west network. A single sensor does not magically see every packet on every part of a switched network.
Internet edge: useful for observing traffic entering or leaving the network.
Server or sensitive network segments: useful for monitoring traffic involving higher-value systems.
Between network segments: useful where segmentation creates meaningful control points.
Cloud or virtual networks: sensors may use virtual taps, mirrored traffic or platform-specific telemetry rather than a physical switch port.
Endpoints: a HIDS can provide visibility into activity that network monitoring cannot see.
What can an IDS alert actually tell you?
An IDS alert tells you that observed activity matched the system's detection logic. That is evidence worth investigating, not automatic proof that a successful cyberattack occurred.
True positive: suspicious or malicious activity occurred and the IDS correctly alerted.
False positive: benign activity matched the detection logic and produced an alert.
False negative: malicious activity occurred but the IDS did not detect it.
True negative: benign activity occurred and correctly produced no alert.
This is why tuning matters. A system that generates an enormous number of low-value alerts can make genuine incidents harder to spot, while overly aggressive suppression can hide useful signals.
Can an IDS detect encrypted traffic?
It can detect some things about encrypted traffic, but encryption limits payload visibility. A network IDS can still analyse information that remains observable, such as addresses, ports, connection patterns, timing, traffic volume and some protocol metadata. What it cannot normally do is read correctly encrypted application content merely because it is an IDS.
Host-based detection can sometimes provide additional context because it operates on the endpoint where data may exist in decrypted form before encryption or after decryption. This is one reason network and host monitoring can complement each other.
Does an IDS slow down broadband?
A passive IDS that receives a mirrored copy of traffic is not normally forwarding the user's packets, so the sensor itself is not an inline throughput bottleneck in the same way an IPS can be. However, the switching, mirroring and monitoring architecture still needs enough capacity to deliver the traffic that the sensor is expected to analyse.
On multi-gigabit networks, capture and analysis capacity becomes important. If a 10 Gbps link can deliver more traffic than the sensor, capture interface or analysis engine can process, packets may be missed. That can reduce detection visibility even though the broadband connection itself continues carrying traffic.
IDS on a home or small-business network
Most ordinary home broadband users do not need to build a dedicated IDS simply to use the internet safely. An IDS becomes more relevant for technically advanced home labs, self-hosted services, businesses, managed networks and environments where additional monitoring is worth the operational effort.
A capable router, firewall or security appliance may already expose some IDS or IPS features. The important questions are what traffic it can actually inspect, whether encrypted traffic limits visibility, how rules are updated, whether alerts are understandable and whether the hardware can keep up with the connection speed.
How to investigate an IDS alert
Read the alert details: identify the rule, timestamp, source, destination, protocol and affected system.
Check the surrounding traffic or host events: one isolated alert rarely provides the whole incident story.
Confirm whether the activity is expected: legitimate scanners, software updates, monitoring tools and unusual applications can trigger rules.
Correlate with other evidence: compare firewall logs, authentication events, endpoint telemetry, DNS activity and application logs where available.
Assess impact: determine whether the suspicious activity merely reached the network or whether it resulted in access, execution, data change or another meaningful outcome.
Tune carefully: suppress or refine noisy detection only after understanding why it fired.
Common IDS misconceptions
An IDS does not automatically block everything it detects.
An alert does not prove that an attack succeeded.
No IDS can guarantee detection of every threat.
Encrypted traffic does not become readable simply because a network IDS is present.
A firewall and an IDS perform related but different security functions.
More alerts do not automatically mean better security.
A sensor can only analyse the activity it can actually observe.
Examples of IDS software
Snort and Suricata are well-known open-source technologies used for network intrusion detection and prevention. Snort describes itself as an open-source intrusion prevention system capable of real-time traffic analysis and packet logging. Suricata describes itself as a high-performance Network IDS, IPS and Network Security Monitoring engine. Both can use rules to generate alerts, and both support capabilities beyond the narrowest definition of a passive IDS.
Key takeaway
An Intrusion Detection System gives you visibility into suspicious activity. A NIDS watches network traffic, a HIDS watches an individual host, and detection logic decides which observed events deserve attention. The crucial point is that detection is evidence for investigation, not proof of compromise and not the same thing as prevention. A useful IDS therefore depends on good visibility, appropriate detection logic, sensible tuning and somebody or something capable of responding to the alerts.
IDS FAQs
What does IDS stand for?
IDS stands for Intrusion Detection System. It is a security system that monitors network or computer activity and analyses it for signs of suspicious behaviour.
Does an IDS block attacks?
A traditional IDS primarily detects and alerts. An IPS can additionally attempt to block or reject matching traffic. Some modern products combine both capabilities.
What is the difference between IDS and firewall?
A firewall enforces rules controlling network traffic. An IDS analyses activity for signs of possible incidents and raises alerts. A single security product can contain both functions, but the concepts are different.
Can an IDS see HTTPS traffic?
A network IDS can observe some metadata about encrypted HTTPS connections, but it cannot normally read the protected application content unless the traffic is deliberately decrypted or terminated at an inspection point.
Is IDS useful on a home network?
It can be useful for advanced home labs, self-hosting and technically managed networks, but it adds operational work. For most households, secure router configuration, updates, strong authentication and appropriate endpoint security are higher priorities.
To explore the related technical concepts used in this IDS (Intrusion Detection System) guide, visit our broadband terminology guide.
